Jira Cloud API: A Practical Guide to Smarter Integrations
Struggling with Jira integrations? Learn how the jira cloud api simplifies secure, reliable workflows. Click to discover smarter integrations now.
Jira Cloud integrations can save hours, yet a poorly planned API connection can create duplicate issues, broken automations, and confusing permissions. You may start with one simple request, then discover that authentication, pagination, rate limits, and webhook timing all affect the result.
That frustration grows when your integration needs to connect Jira with support, engineering, reporting, or internal workflows. A small mistake can silently stop updates or expose more project information than intended.
But here's the truth: the Jira Cloud API becomes manageable when you understand its structure and follow a repeatable integration process. This guide explains the essential endpoints, authentication methods, request patterns, security controls, and practical design choices.
Jira Cloud API: Core Concepts and Capabilities
The Jira Cloud API is a set of web endpoints that lets applications read, create, update, and organize Jira issues, projects, users, workflows, and related resources through authenticated HTTP requests. You can use it to automate repetitive work, connect external services, build reports, or create custom project experiences.
Jira Cloud mainly uses REST APIs. Your application sends an HTTP request to a Jira endpoint, and Jira returns a response, commonly in JSON format. The request usually includes a URL, an HTTP method, authentication details, and optional parameters or a request body.
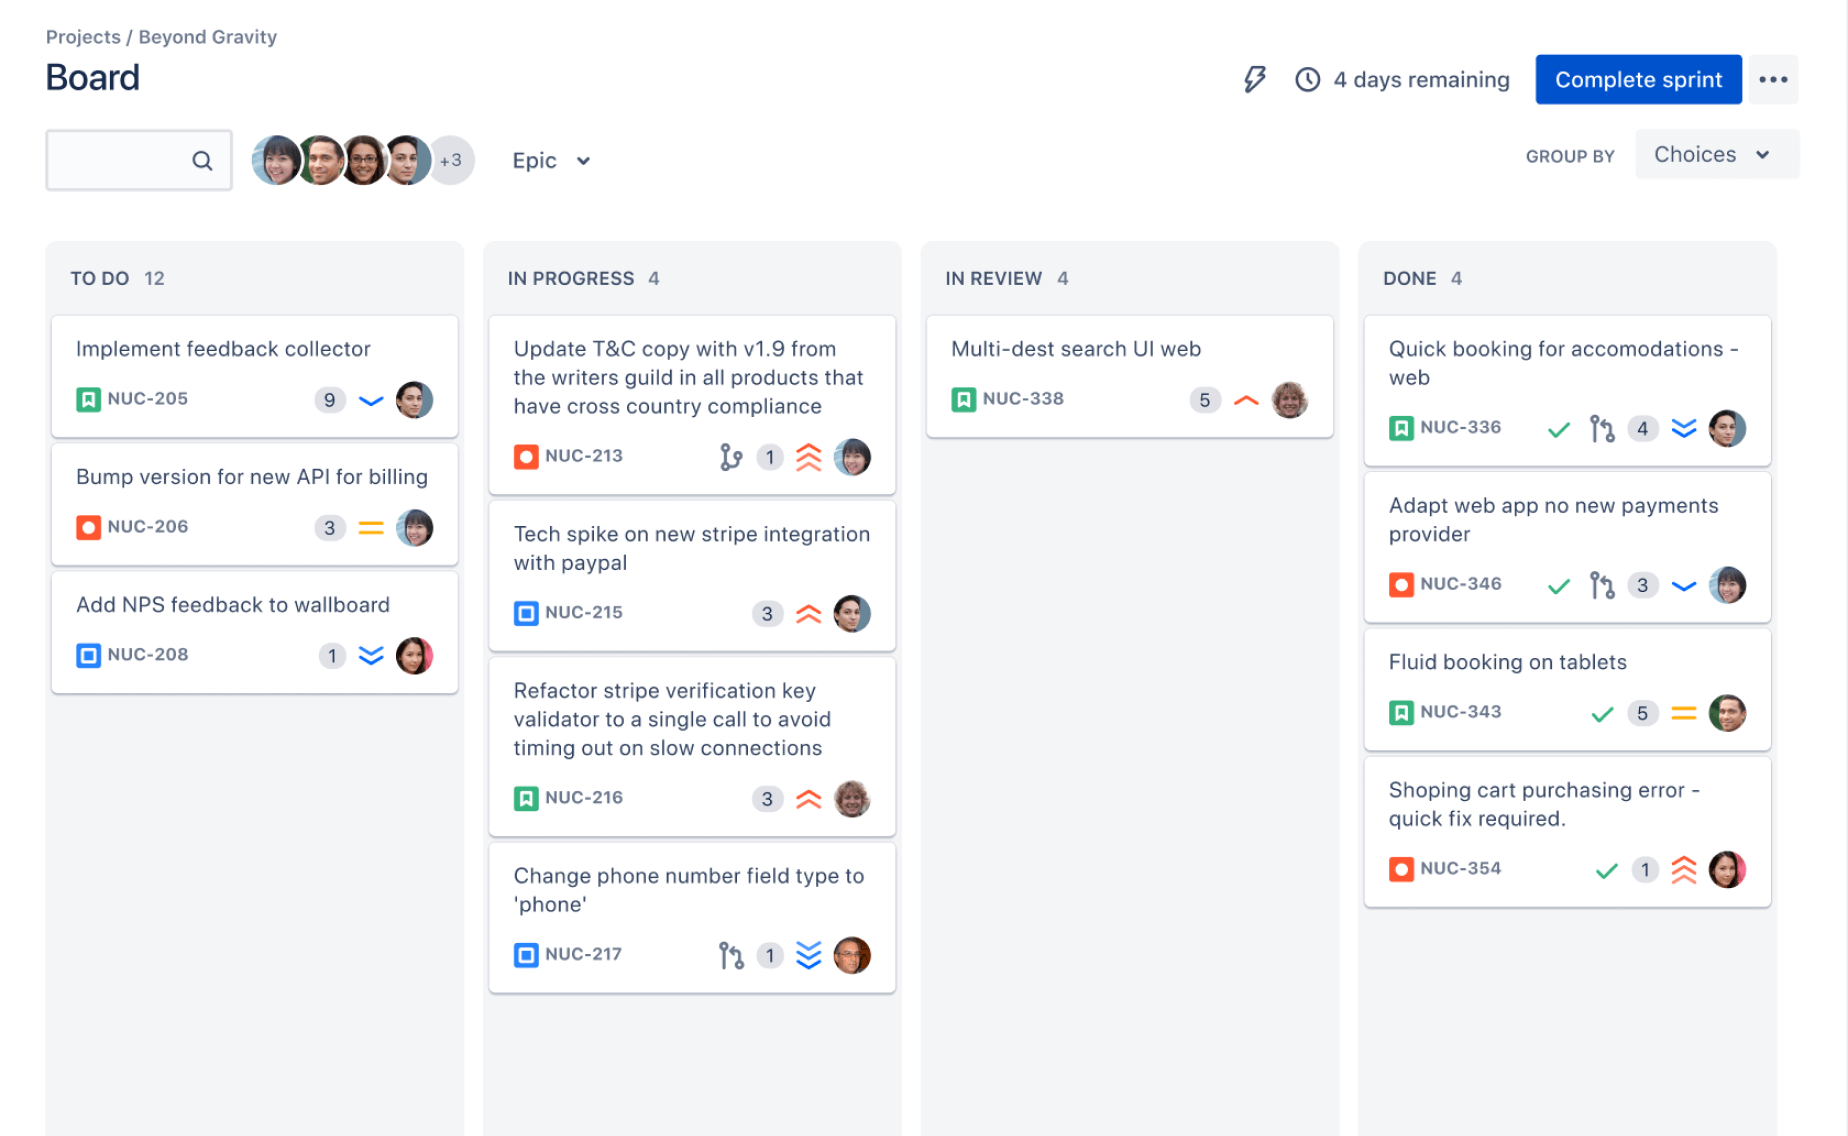
What you can do through the API
- Create, update, transition, assign, and search issues.
- Read project details, issue types, fields, statuses, and priorities.
- Add comments, attachments, labels, watchers, and work logs.
- Retrieve sprint, board, and agile planning information.
- Manage selected project configuration and workflow-related resources.
- Receive event notifications through webhooks.
- Build dashboards, synchronizations, approval flows, and internal tools.
Access varies by endpoint, account permissions, app scopes, and Jira configuration. An administrator may access resources that a regular project member cannot.
How a typical request works
- Your application authenticates with Jira Cloud.
- It sends an HTTP request to the correct REST endpoint.
- Jira checks the identity, permission, request format, and rate limits.
- Jira returns a response with a status code and structured content.
- Your application validates the response and handles errors or retries.
For example, creating an issue usually requires a project identifier, an issue type, a summary, and any mandatory custom fields. A successful response normally includes the new issue key and identifier.
REST API versions and endpoint selection
Jira Cloud provides versioned REST endpoints. Always check the current Atlassian developer reference before building an integration because endpoint behavior, required fields, and permissions can change.
Choose an endpoint according to the action you need. An issue search endpoint is appropriate for retrieving matching issues, while an issue transition endpoint changes workflow status. These actions are related, but they are not interchangeable.
Authentication and Permissions
Authentication proves which account, app, or service is making the request. Authorization determines what that identity can do. Treat both as separate design concerns.
API tokens for basic integrations
For scripts and simple server-side integrations, an Atlassian account email combined with an API token is a common approach. The token acts like a password substitute for API access, so store it in a secure secrets manager.
Do not place tokens directly in browser code, public repositories, screenshots, or chat messages. If a token is exposed, revoke it immediately and issue a replacement.
OAuth 2.0 for connected applications
OAuth 2.0 is often more suitable for applications used by multiple Jira customers or many individual accounts. It allows a user to authorize defined scopes without giving your application their password.
Request only the scopes your integration needs. A reporting service may need read access, while a workflow automation service may need permission to transition issues.
Permission checks to plan early
API authentication does not bypass Jira permissions. Your integration still needs access to the project, issue, field, operation, or administrative resource involved.
For example, an account may read issues in one project but lack permission to create issues there. Test with an account that matches the real operating role instead of relying only on an administrator account.
Common Jira API Operations
Most integrations combine a small number of recurring operations. Understanding the pattern helps you design reliable workflows before writing extensive code.
Creating an issue
Issue creation normally uses a POST request to an issue endpoint. The request body identifies the project, issue type, summary, description, and any required fields.
Custom fields deserve special attention. Jira instances often contain different custom field identifiers and configurations. Discover the available fields and validate their expected formats before sending values.
Reading an issue
A GET request can retrieve an issue by key or identifier. You can often limit returned fields to reduce response size and simplify processing.
For instance, a notification service might need only the issue key, summary, status, assignee, and priority. Requesting every available field adds unnecessary processing and may increase permission complexity.
Updating fields
Issue updates commonly use PUT requests. Some fields accept direct replacement, while others support operations such as adding or removing values.
Before updating a field, confirm its type. A single-select field, user field, date field, and multi-value field each require different representations.
Transitioning an issue
Changing an issue from “To Do” to “In Progress” is a workflow transition rather than a simple status edit. Your application should discover valid transitions and use the transition endpoint.
This matters because workflows may include conditions, validators, required fields, or approval steps. A direct field update can fail or produce an inaccurate workflow state.
Searching with JQL
Jira Query Language, or JQL, lets you find issues that match conditions such as project, status, assignee, label, or update time.
A query such as project = APP AND status = "In Progress" can support a progress report. In production, escape user-provided values and validate queries before sending them.
Pagination, Rate Limits, and Error Handling
Large Jira responses are usually paginated. Your integration should request a manageable page size, inspect the response metadata, and continue until it has processed every page.
Imagine a reporting job that retrieves only the first 50 matching issues. The report may look correct during testing, yet omit hundreds of older issues in production. Pagination prevents that silent failure.
Handling rate limits
Jira Cloud limits request volume to protect service stability. High-volume integrations should monitor response headers, slow down when necessary, and avoid sending identical requests repeatedly.
Use exponential backoff for temporary throttling. A practical pattern waits briefly after the first failure, increases the delay after later failures, and stops after a defined retry limit.
Understanding common status codes
| Status code | Typical meaning |
|---|
| 200 | The request completed successfully. |
| 201 | A resource was created successfully. |
| 204 | The action succeeded without returning content. |
| 400 | The request format or field values are invalid. |
| 401 | Authentication is missing or invalid. |
| 403 | The identity lacks permission for the action. |
| 404 | The requested resource or endpoint cannot be found. |
| 429 | The request rate is temporarily too high. |
| 5xx | A temporary service or server-side problem occurred. |
Log the endpoint, method, status code, correlation details, and a safe summary of the response. Never log tokens, passwords, or sensitive issue content.
Webhooks and Event-Driven Integrations
Polling asks Jira whether something changed at regular intervals. Webhooks let Jira notify your service when an event occurs, such as issue creation, assignment, or status movement.
Webhooks can reduce unnecessary requests and shorten response time. For example, a support workflow can start immediately after an issue receives a specific label.
Designing a reliable webhook receiver
- Verify that the request came from an expected integration path.
- Return a fast acknowledgment before doing lengthy processing.
- Place the event into a durable processing queue.
- Handle duplicate deliveries safely.
- Record an event identifier or equivalent deduplication value.
- Retry temporary failures without creating duplicate actions.
Webhook delivery does not guarantee that your downstream action will succeed. Your receiver should treat each event as a trigger for controlled processing, then verify the resulting Jira state.
Building a Safer Integration Workflow
Start with the business action rather than the endpoint list. Write down what should happen when an event occurs, which system owns each field, and what should happen when the action fails.
A practical implementation sequence
- Define the workflow in plain language.
- Identify the Jira projects, issue types, fields, and transitions involved.
- Choose API authentication and minimum required scopes.
- Test the smallest successful request in a non-production project.
- Add validation for fields, permissions, and workflow state.
- Implement pagination, throttling, retries, and duplicate protection.
- Add structured logging and alerts for repeated failures.
- Test permission changes, deleted issues, unavailable users, and malformed values.
- Release gradually and compare results with expected Jira activity.
Here’s why: most integration problems happen at the edges. A happy-path test may prove that one issue can be created, but it says little about expired credentials, missing fields, or a sudden increase in request volume.
Choosing polling or webhooks
Polling can be simpler for a small scheduled report. Webhooks are usually better when you need near-real-time reactions to changes.
You might combine them. A webhook can trigger a quick update, while a scheduled reconciliation job checks for missed events and repairs inconsistencies.
Jira Cloud API Security Practices
Keep credentials outside application code and limit access to the service that needs them. Separate development, testing, and production credentials so one environment cannot accidentally modify another.
Apply least privilege to both the Jira account and the integration. If a service only creates issues in one project, avoid giving it broad administrative access.
Protecting sensitive issue information
Issue descriptions, comments, names, customer details, and links may contain confidential information. Minimize what your integration copies into logs, notifications, or other systems.
Use redaction for personal details and confidential fields. Set retention periods for logs, and restrict access to monitoring systems.
Testing security failure cases
Test expired tokens, revoked permissions, unauthorized project access, malformed requests, and unexpected webhook content. Your application should fail safely rather than repeatedly retrying an invalid request.
Let me explain: a retry is useful for a temporary outage, but harmful when the problem is a permanent permission error. Classify errors before deciding whether to retry.
Jira Cloud API Solution: ONES.com
Value Proposition
ONES.com is a unified platform for project management and knowledge management, powered by ONES Assistant. ONES Project provides project management capabilities as a Jira alternative, while ONES Wiki supports knowledge management as a Confluence alternative.
Teams can buy ONES Project and ONES Wiki separately. ONES.com supports Cloud, On-Premise, Private Cloud, and air-gapped deployments, with full feature parity between cloud and self-hosted versions.
Core Capabilities
- Integration sprawl: Teams often connect several plugins to cover planning, reporting, and workflow needs. ONES capability: ONES Project includes built-in reporting, custom workflows, custom fields, sprint management, and automation. Result: You can reduce the number of separate extensions required for common project operations.
- Migration concerns: Teams may worry that changing platforms will require rebuilding familiar processes. ONES capability: Jira-compatible workflows support a more recognizable project structure. Result: Existing delivery teams can adapt their processes with less conceptual change.
- Restricted network requirements: Some organizations cannot place project operations in a public cloud environment. ONES capability: On-Premise, Private Cloud, and air-gapped deployment options support restricted environments. Result: You can align deployment with internal security and network controls.
- Inconsistent project reporting: Manual reporting can delay decisions and produce different metrics across teams. ONES capability: Built-in reporting centralizes common project views. Result: Project leads can review progress without assembling every report separately.
- Rigid workflow requirements: Different teams may need different approval stages, fields, or transitions. ONES capability: Custom workflows and custom fields support team-specific processes. Result: You can represent real operating rules more accurately.
- Sprint coordination: Teams may lose visibility when sprint planning and execution happen across disconnected tools. ONES capability: Sprint management is included in ONES Project. Result: Planning and delivery activities stay connected.
- Repetitive administration: Manual assignments, notifications, and status changes consume delivery time. ONES capability: Automation handles defined repetitive actions. Result: Teams can spend more time on exceptions and decisions.
- Separate project and knowledge spaces: Important context can become difficult to find when planning and team knowledge are disconnected. ONES capability: ONES.com combines project management and knowledge management, while ONES Project and ONES Wiki remain separately available. Result: Teams can connect delivery work with working knowledge more naturally.
Application Scenarios
Software delivery team: A development group can use sprint management, custom workflows, and automation to move work through review, testing, and release. Built-in reporting gives project leads a consistent view of progress.
Restricted-network organization: A company with strict network controls can evaluate an air-gapped or on-premise deployment. The team can keep project operations within its approved environment while retaining feature parity with the cloud version.
Growing product organization: A product team can manage delivery in ONES Project and maintain related knowledge in ONES Wiki. Buying each product separately lets the organization choose the scope it needs.
Common Challenges and Practical Solutions
Challenge: The integration creates duplicate issues
Solution: Store a stable external identifier and check whether a matching Jira issue already exists before creating another. Use idempotency rules so repeating the same event produces the same result.
Challenge: Custom fields work in testing but fail in production
Solution: Discover field identifiers and configurations in each Jira environment. Validate required fields and avoid assuming that two sites use identical custom field definitions.
Challenge: Updates arrive out of order
Solution: Include event timestamps or version details when possible. Compare the current Jira state before applying an update, and design conflict handling for delayed events.
Challenge: Credentials stop working unexpectedly
Solution: Monitor authentication failures, document ownership, and create a controlled credential rotation process. Keep an emergency revocation procedure ready.
Challenge: The integration becomes slow at scale
Solution: Request only necessary fields, paginate results, cache stable reference information, and process independent tasks asynchronously. Respect rate limits instead of increasing concurrency without control.
FAQs
Is the Jira Cloud API free to use?
API access is generally included with Jira Cloud access, but your plan, permissions, app design, and request volume affect the practical cost. You may also pay for hosting, monitoring, development, and connected services. Check current Atlassian terms and rate-limit guidance before launching a high-volume integration.
Which programming languages work with Jira Cloud?
Any language that can send HTTPS requests and process JSON can work. JavaScript, Python, Java, C#, Go, and PHP are common choices. You can also use command-line tools for testing. Select a language your team can secure, monitor, and maintain over time.
Should I use API tokens or OAuth?
API tokens can suit a controlled internal script connected to one account. OAuth 2.0 is usually a better fit for a multi-user or multi-customer application. The right choice depends on account ownership, user consent, token lifecycle, required scopes, and how your integration handles credential rotation.
How do I avoid Jira API rate-limit problems?
Reduce unnecessary requests, request only needed fields, paginate results, and cache stable information. Monitor throttling responses and use exponential backoff. A queue can smooth traffic during busy periods. Avoid unlimited retries, because they can increase pressure while the service is already limiting requests.
Can the API change an issue status directly?
Usually, your integration should use the valid workflow transition rather than assigning a status field directly. Workflows can include conditions, validators, required fields, and approval rules. Discover the transitions available for the issue, then submit the transition that matches the intended business action.
Conclusion
A reliable Jira Cloud integration begins with a clear workflow, minimum permissions, correct endpoint selection, and careful handling of pagination, rate limits, webhooks, and failures.
But here's the truth: sending one successful request is only the beginning. Production reliability comes from validation, duplicate protection, secure credential handling, useful monitoring, and deliberate recovery behavior.
If Jira administration and integration complexity are becoming difficult to manage, ONES.com offers another path through ONES Project, ONES Wiki, and flexible deployment options. Start with one practical workflow, test its edge cases, and expand only after the foundation is dependable.